
2027 Security Planning:
What Matters Is Real Security Impact
AI-driven threats are getting more sophisticated. Your defense needs AI too.
Xint reproduces real attacks to find the vulnerabilities that actually get through, and tells you exactly how to fix them.
Xint reproduces real attacks to find the vulnerabilities that actually get through, and tells you exactly how to fix them.

INTRODUCING XINT
Continuous Pentest-grade Security
From Source to Runtime
Xint finds exploitable vulnerabilities in source code, validates them in running applications,
and returns proof your team can act on.
The depth of a pentest at the speed of automation.
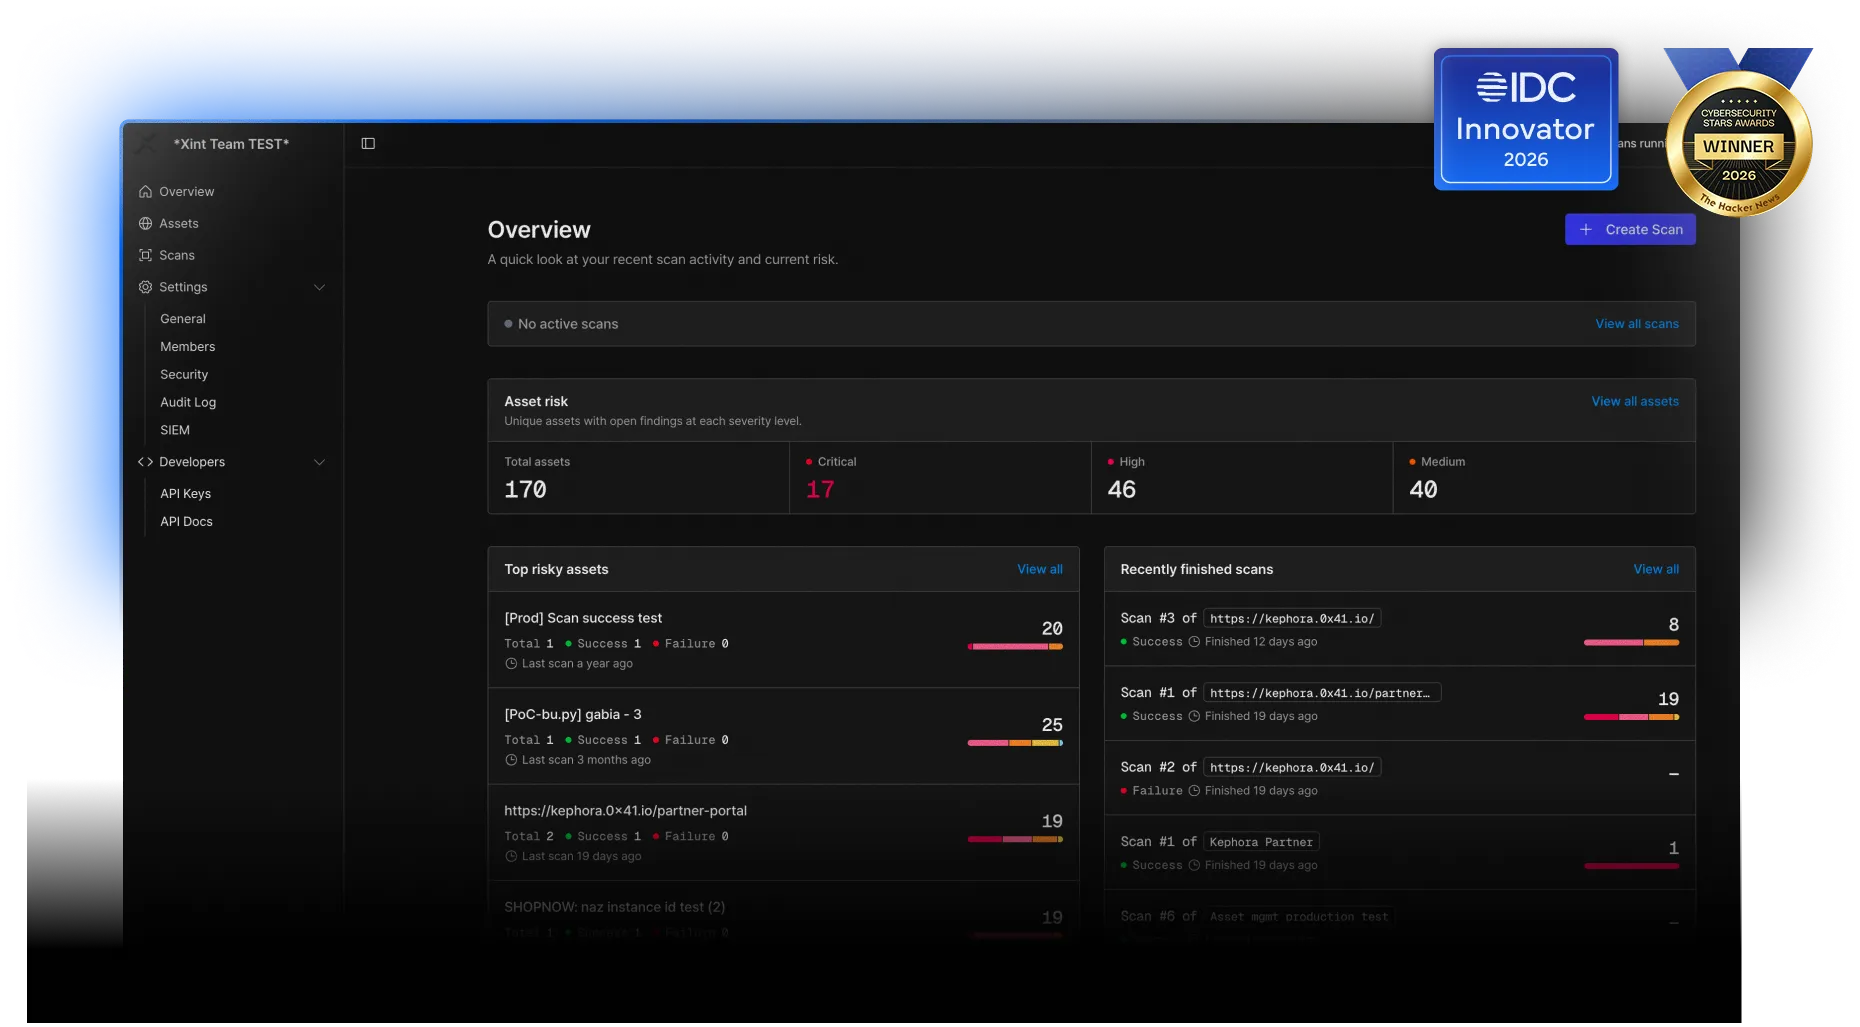

Exploitable by Design
Every finding is a real exploit.
If Xint surfaces it, an attacker
can use it.
If Xint surfaces it, an attacker
can use it.

Fully Reproducible
Each vulnerability ships with reproduction steps so your team can verify it immediately.

Offensive Expertise at Scale
Xint is built on real pentester methodology to find complex,
multi-step attack chains.
multi-step attack chains.
Everything you need for your budget report, in one request
Try Xint free before you buy and find out whether your service has vulnerabilities an attacker could actually exploit.

Xint Overview
A detailed introduction to the Xint platform, its features, and technology

Custom Quote
A quote tailored to your targets and scale

Sample Report
A real report template with vulnerabilities, exploit reproduction code, and patch guidance
CUSTOMER REVIEWS
Why security teams choose Xint

Adopting Xint validated our robust security posture, ensuring compliance with major global standards like MDSAP and ISO/IEC 27001/27701. The platform allowed us to continuously elevate our product security throughout its lifecycle via regular vulnerability assessments and re-verifications, maintaining strict compliance with FDA requirements.

We required flexible application testing to handle surge periods around product launches, ensuring a secure and seamless customer experience. Xint Pulse solved this by delivering results in hours. By supplying full trigger conditions, POC code, and detailed exploit impact reports, it enabled our team to prioritize and resolve critical issues instantly.
Your 2027 Security Budget:
Measure Results, Not Spend
See for yourself whether Xint actually makes your service safer.

Get a Custom Quote
Get a Custom Quote
→